Classic McEliece's Security Margins Just Collapsed. Here's What That Proves About Crypto-Agility.
 Classic McEliece's Security Margins Just Collapsed. Here's What That Proves About Crypto-Agility.">
Classic McEliece has stood for 48 years. Built on binary Goppa codes in 1978, it was the longest-standing candidate in NIST's post-quantum standardisation process and widely regarded as the most conservative choice available. BSI recommended it from 2020. ISO standardised it in June 2026. Serious organisations deployed it. No structural attack had come anywhere near its claimed security levels in nearly five decades.
That changed in a matter of weeks. In August 2026, Ghoshal, Ishai, Jain and Sun published the first distinguisher for Classic McEliece public keys that costs less than brute-force decoding. Weis then showed that the distinguisher computation already contains the secret key, and gave two methods to extract it. The cost of key recovery now falls below Classic McEliece's claimed security levels in the standard bit-operation model: 2^94 to 2^102 against claimed levels of 2^143 to 2^272.
What this means, precisely: the theoretical security margins that Classic McEliece relied on no longer hold. The attacks are not practically executable today (the paper is explicit: "none of this is close to practical"), and the scheme could be salvaged with larger parameters. But the margin that everyone was counting on evaporated in a matter of weeks.
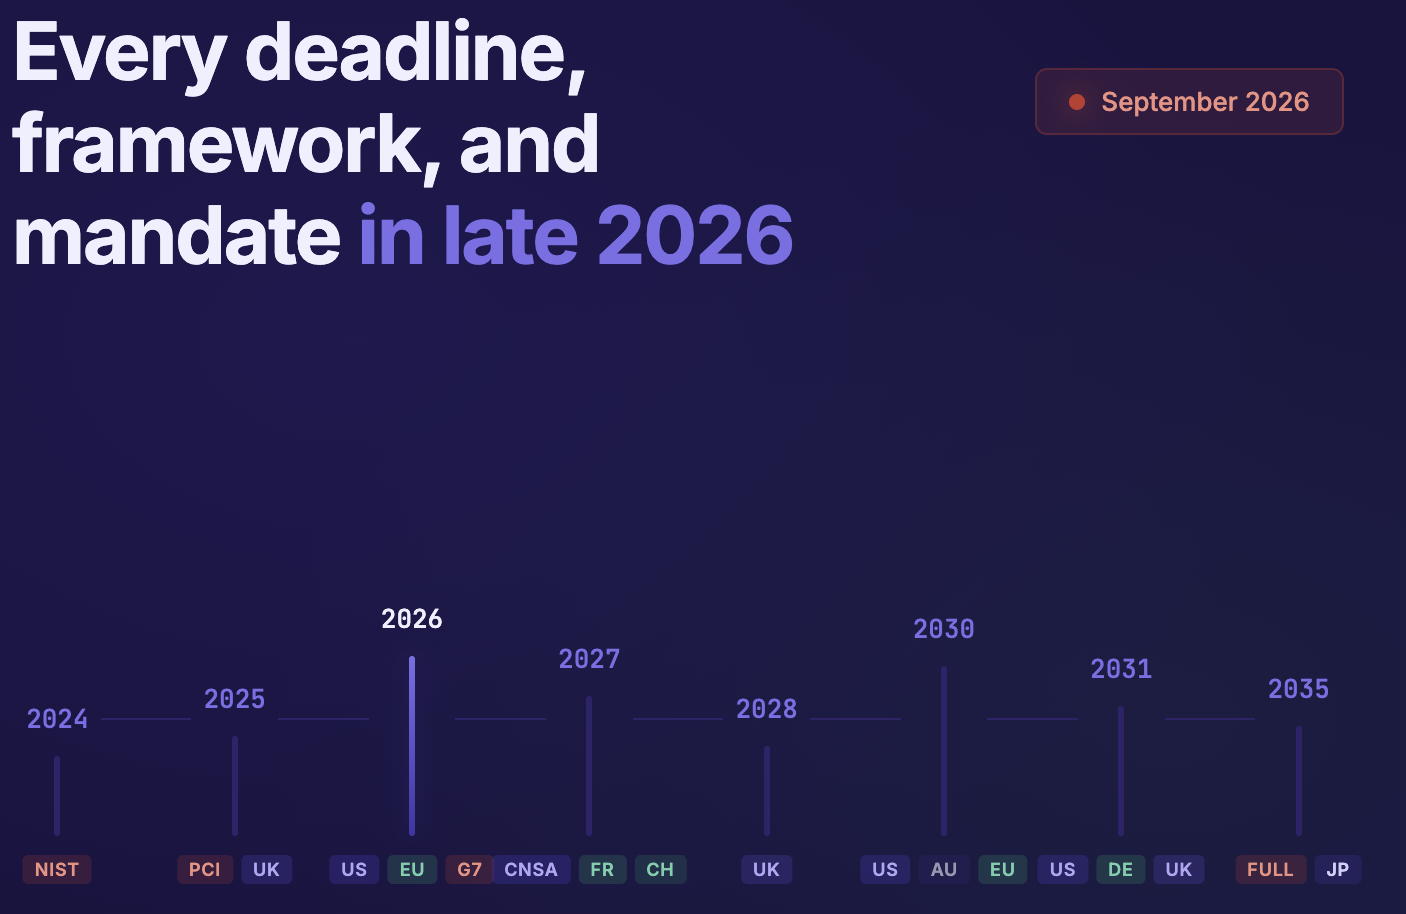
On October 1, Germany's BSI advised against using Classic McEliece in new developments. It had recommended the scheme since 2020. ISO had standardised it four months earlier. The reversal took 55 days from the first credible paper.
That is not a "the algorithm is dead, panic now" situation. It is something more instructive: a case study in how fast cryptographic confidence can erode, and what that demands of the organisations that depend on it.
This is not a post-quantum problem
This is a crypto-agility problem. The organisations that deployed Classic McEliece made a defensible choice at the time. The question now is whether they can assess their exposure and, if needed, change course without a multi-month re-architecture.
As we argued in our recent piece for KBI Media, post-quantum is the wrong frame for crypto-agility. Framing everything as "get to PQC" treats algorithm selection as the destination. Classic McEliece was a post-quantum algorithm. It passed every review. It was the destination, and the destination just shifted.
The real capability to build is the ability to detect, assess and replace cryptographic primitives when the landscape changes. Not once, on a project timeline. Repeatedly, as a continuous organisational function.
What does "agility" actually look like in practice?
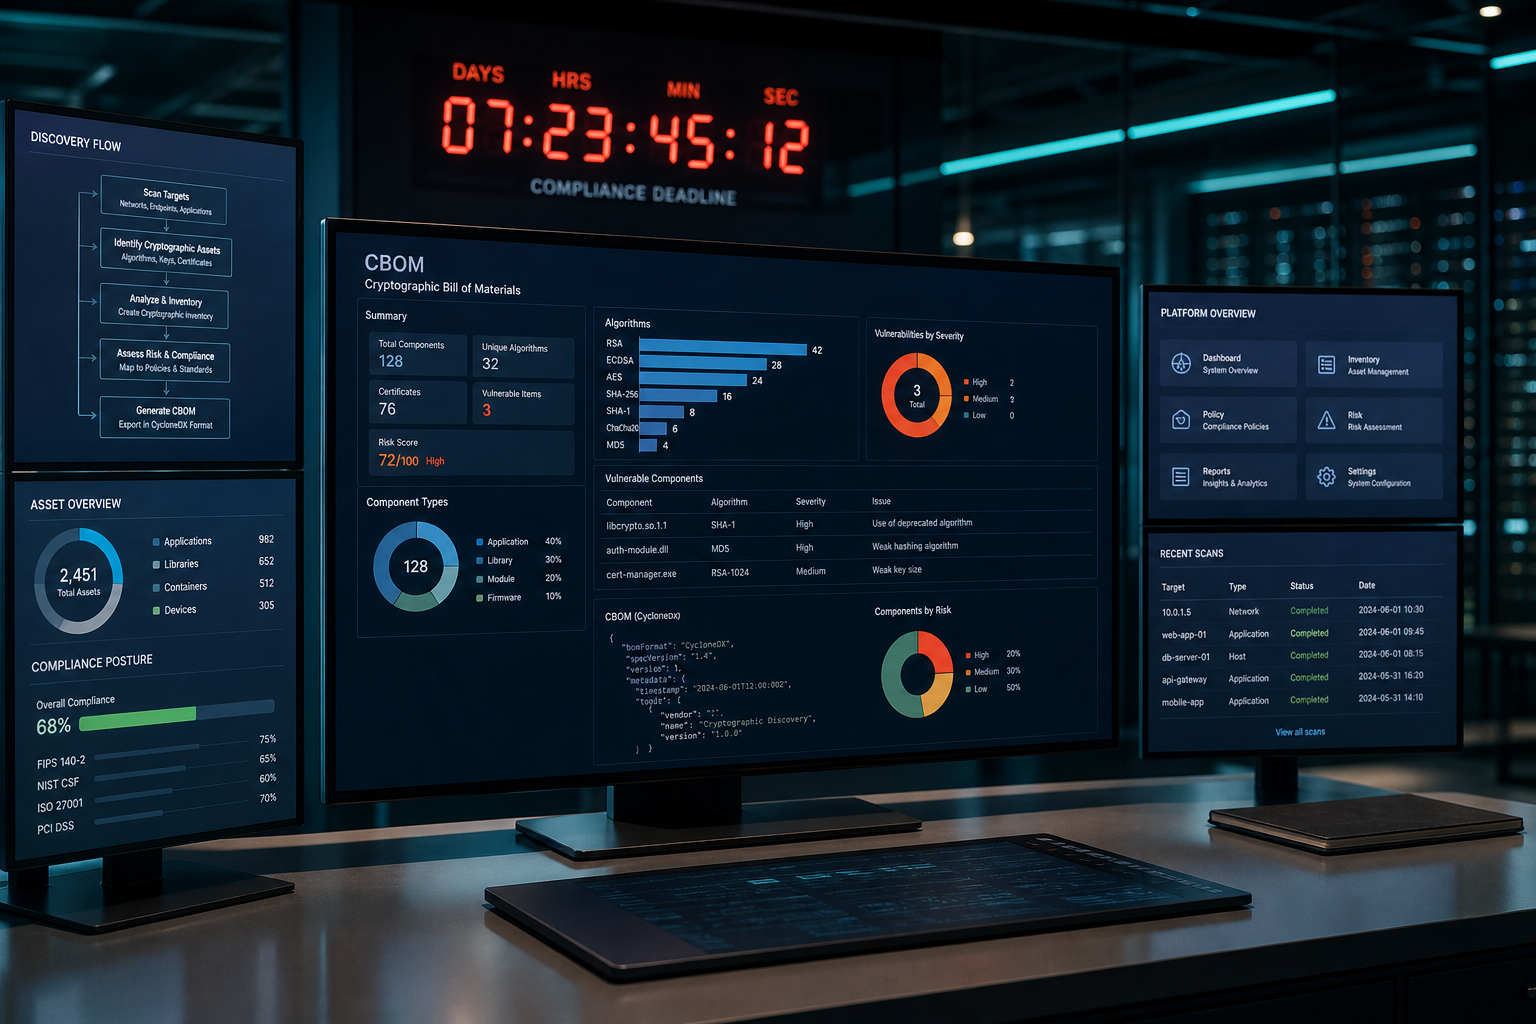
It starts with knowing what you have. If you cannot enumerate where Classic McEliece (or any algorithm) appears in your estate, you cannot assess your exposure when a paper drops on ePrint. A Cryptographic Bill of Materials is the foundation: every key, certificate, protocol version and algorithm mapped, scored and tracked over time.
It continues with having a migration path that does not require a six-month re-architecture. Organisations that built their PQC integration around a single algorithm with no abstraction layer will face exactly that problem if confidence erodes further. Organisations that adopted an agile cryptographic architecture, where the algorithm is a configuration choice rather than a structural dependency, can rotate within days.
And it requires staying informed. The gap between a paper appearing on IACR ePrint and a national authority reversing its recommendation was 55 days. That is shorter than most procurement cycles. Classic McEliece went from "no structural attack within range" to "BSI advises against new deployments" in under two months.
What we are building to close this gap
We have designed CipherWatch, our monitoring surface inside the EQCore platform, to address exactly this problem. CipherWatch is now a curated PQC threat-intelligence feed: cryptanalytic developments, regulatory updates and compliance guidance, published globally by our team and regionally by our partners for their own clients.
Items are filtered by region, so an Australian client sees ASD ISM updates alongside global news like the McEliece papers. A Malaysian client sees NACSA Directive 9 changes. A Canadian client sees Bill C-8 developments. A German client would see the BSI reversal the day it happened. Partners contribute content for their own jurisdictions, making the feed richer as the network grows.
The Classic McEliece story is a clear example. That development appearing inside CipherWatch, with the context to understand what changed and what it means for your estate, is the difference between a CISO reading about it weeks later and a security team assessing their CBOM exposure while the implications are still being understood.
Crypto-agility is not a feature. It is an organisational capability. But capabilities need infrastructure, and that infrastructure needs to match the actual clock speed of the domain. Cryptographic confidence moves at the pace of research papers, regulatory calendars and compliance deadlines. CipherWatch is built to match that pace.
If you want to understand how your organisation's cryptographic estate would respond to a development like Classic McEliece, start with a conversation.